Sovereignty Is Decided on the Edges

The Cloud and AI Development Act, CADA, proposed in June, would require European public bodies in the categories it singles out to buy cloud at a recognised assurance level set by a risk assessment. How that assessment should be done is not in the proposal. It is left to follow-up rules that do not exist yet.

The Cloud Sovereignty Framework the Commission published in October 2025 leaves the same gap. It runs to six pages, defines eight sovereignty objectives, and grades a tenderer’s cloud services on each using Sovereignty Effectiveness Assurance Levels, from SEAL-0 (“No Sovereignty”) to SEAL-4 (“Full Digital Sovereignty”). The buyer sets a minimum level for each objective. Miss one, and the tender does not qualify. The framework never says how a buyer is to arrive at the minimums. It is already in use: in April 2026 the Commission awarded the first contracts assessed under it, grading three bidders building their own technology at SEAL-3 and a fourth, whose service runs on Google Cloud technology, at SEAL-2.
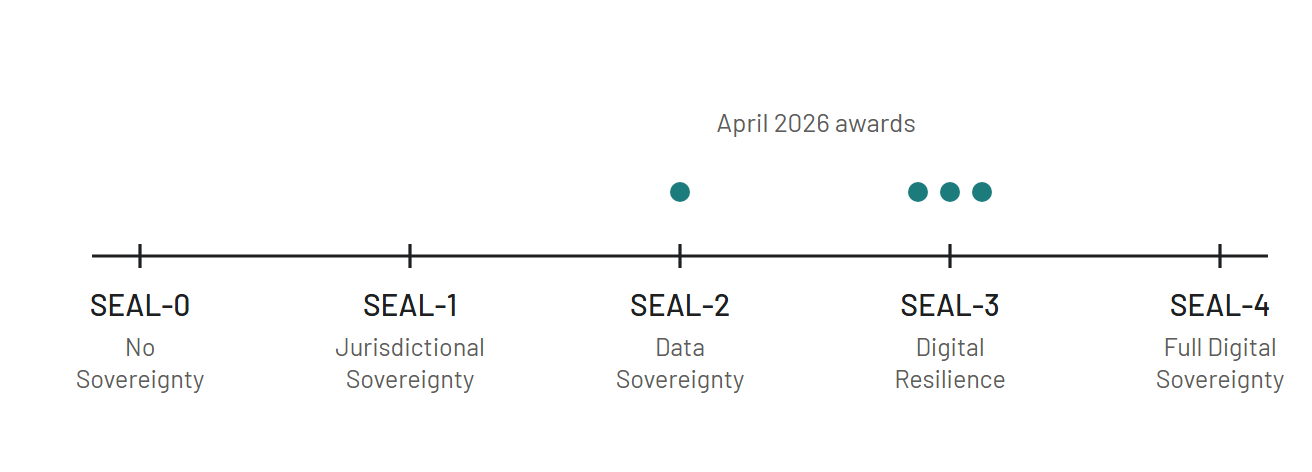
The five Sovereignty Effectiveness Assurance Levels on one scale, from SEAL-0 No Sovereignty to SEAL-4 Full Digital Sovereignty. Dots mark the April 2026 awards: three providers at SEAL-3, one at SEAL-2.
The framework’s five levels, and where the April 2026 awards landed. Source: European Commission.

In those six pages, exactly one sentence concerns which of the buyer’s own systems can go where. It says the results “may also be used”, by the buyer’s own technical services during the contracts that come out of the same tender, “to determine the nature of systems that can be deployed at a specific provider, different risk profiles requiring different assurance levels”. That is the whole of it, and it presupposes the risk profiles already exist.

Meanwhile the labelling goes on. Across Europe, organisations are sorting their applications into “sovereign” and “standard”, one row at a time, and filing the result. The file records what each application is, never what it stands on.

What the file misses shows up the first time a boundary closes.

Continue reading “Sovereignty Is Decided on the Edges”

Multi-Cloud and Omni Cloud Are Not the Same Thing

Title card: card-2790

The digital horizon is constantly evolving, and at its forefront is the transformative power of cloud computing. Terms like “multi-cloud” and “omni cloud” are not mere buzzwords but signify strategic shifts in how businesses approach their digital infrastructure. This article demystifies these strategies, placing them under the lens for a clearer understanding.

Tracing the Cloud Evolution

From the dawn of mainframe computers to the advent of internet-based cloud solutions, the narrative of cloud computing has been one of innovation and adaptation. Initially, the focus was singular – one business, one cloud provider. Today, the narrative champions competition, diversity of services and integration.


Defining Multi-Cloud

Multi-Cloud is the strategy of using multiple cloud providers, where each provider handles a separate, distinct workload or application. The motivation is often to avoid vendor lock-in, leverage specific features of each provider, or to ensure redundancy and risk distribution.

Continue reading “Multi-Cloud and Omni Cloud Are Not the Same Thing”

Developer Autonomy Is a Platform Decision

Title card: card-2766

Most companies want to be able to innovate and grow quickly. But the ability to do so depends on the organization’s ability to balance developer autonomy with platform manageability and security. It’s not an easy task, but one that requires careful planning ahead of time. Here are principles every company should follow on their cloud journey:

The cloud is how companies innovate, scale and grow.

The cloud is how companies innovate, scale and grow. As a result, it’s important to balance developer autonomy with manageability of the platform. By allowing developers the freedom to create and innovate, you can get more out of your investment in technology. However, without proper controls and security measures in place, there are risks associated with this approach as well.

The cloud allows for continuous innovation through agile development practices—the ability for teams to rapidly develop new features or products that allow them to move faster than ever before. As a result of this rapid innovation cycle, developers need access to tools that allow them to keep up with changes across multiple programming languages (like Python, Terraform, Cloud Providers Native Languages) while ensuring compliance with industry standards like ISO, GXP, PCI-DSS or NIST regulations

The shift to the cloud can be overwhelming and confusing, especially as many organizations find themselves with a multi-cloud environment, which can lead to it’s own set of challenges.

Continue reading “Developer Autonomy Is a Platform Decision”

Azure Governance Never Finishes

Title card: card-2528

In this blog post, we will discuss the management and operational principles which underpin enterprise governance in Azure which is a necessity for successful cloud adoption and one of the first rails to enable a culture that facilitates digital innovation.

The core components of Azure management are the challenges of Enterprise Cloud Adoption and the components which make up the full set of governance capabilities in Microsoft Azure.

The Azure governance principles are a continuum of tasks, projects and initiatives, therein you build natively in Cloud and also migrate workloads into Azure, securing and protecting those workloads so that they are robust and resilient. You then proceed to monitoring these workloads, so that you can pick up any problems and ensure that they are consuming resources in a manner which is both performant and cost-effective.

Next, you invest in automated configuration to ensure that any changes to your workloads are holistic but also auditable and immutable. Governance ensures that your workloads and the platform on which they run are compliant with your company’s policies and regulatory obligations. This, in turn, creates a more robust enterprise platform, ready to receive new workloads and in turn, a becomes a hub for innovation with the necessary guard rails in place.

Continue reading “Azure Governance Never Finishes”

In China, Someone Else Operates Your Cloud

Title card: card-2519

When Westerners think of hyperscale cloud providers, the usual suspects that come to mind are named Amazon Web Services, Microsoft Azure, Google Cloud Platform, Oracle, and IBM Cloud. Seldom do you hear another name, which tends to be odd since it is already the world’s third-biggest cloud service provider according to the numbers: Alibaba Cloud. And with yearly revenue growth between 60 and 140%, they sure are catching up fast.


Blog_AWS-vs-GCP-vs-Azure-vs-Alibaba


However, to operate a cloud within China there are some hoops you need to jump and you have to collaborate with the regional administration. Provisioning and relocation times, thus, are fundamentally increased, in no little part since tasks must be directed by the local partners. The truth of the matter is that, while it is conceivable, receiving a cloud foundation that does not have a physical presence in China places organizations that operate in China at a colossal detriment.

Continue reading “In China, Someone Else Operates Your Cloud”

Security Questions to Settle Before a Migration

Title card: card-2444

Information security aspects when moving operations from on-premise

So if you are reading this I will make some basic assumptions that you know about Microsoft Azure, Amazon Web Services and perhaps even Alibaba Cloud, these are renowned hyperscale cloud vendors. Last few years cloud computing have been among the IT industries hottest topics. The term refers to on-demand access to computing resources provisioned by another provider. 2019 has been dubbed the year of migrations by several vendors and a pronounced advantage of cloud computing is that they tend to be highly available and easily scalable. For fast-growing business, cloud-computing has revolutionized the way they can work. Organizations typically lease cloud-based resources from outside the organization. Of course, it is also possible (but not as common) to host cloud-based services internally.

While cloud computing can be very cost-efficient and offer fast scaling, it’s challenged by the fact that resources will most likely be hosted outside of the business’ data centre and therefore, outside of the direct control of that business, increasing the complexity to manage risk and handle governance.

Continue reading “Security Questions to Settle Before a Migration”